Civil-liberties lawyer Cindy Cohn and security technologist Bruce Schneier have called for a broad reassessment of mass surveillance in the United States, arguing that systems developed after the September 11 attacks have expanded far beyond their original national-security rationale.
In an essay published on September 15, the authors contrast surveillance aimed at a particular person with techniques that gather information across entire networks or populations. They say the post-2001 shift included bulk collection of telephone and internet metadata and interception at major telecommunications links. In their account, those methods are no longer confined to counterterrorism programs.
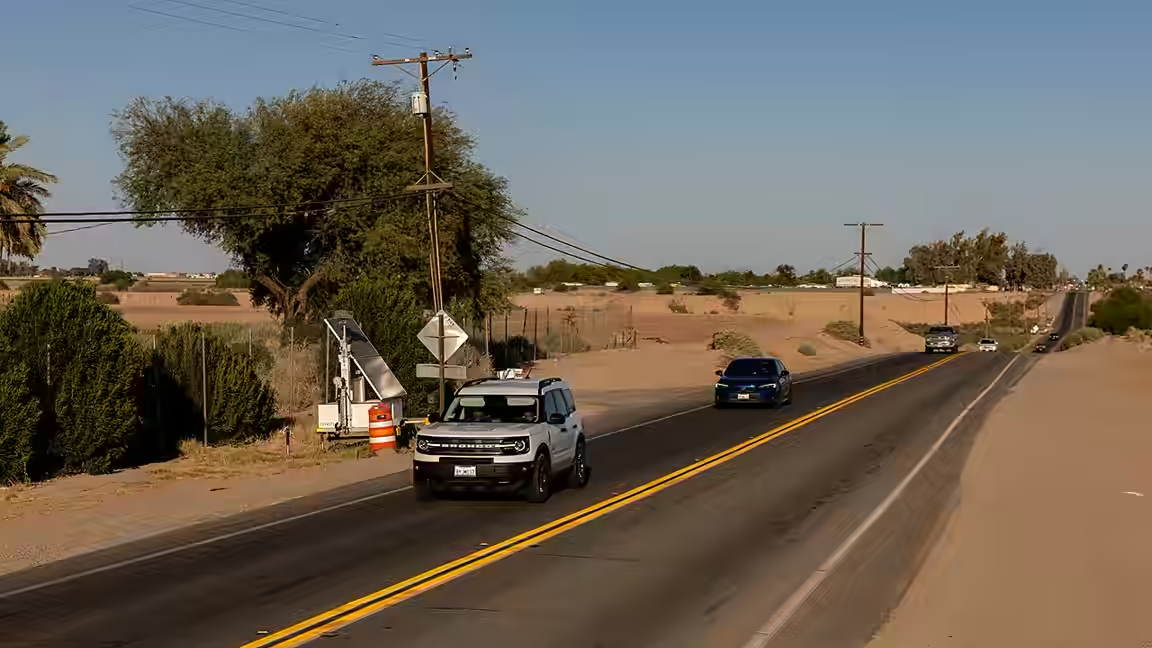
Cohn and Schneier point to immigration enforcement, local policing and privately operated systems as parts of the same expanding ecosystem. Their examples include facial-recognition systems at venues, networked license-plate readers and the purchase of commercial data by government agencies. The essay argues that the distinction between corporate and state surveillance has become increasingly porous because public authorities can obtain information first collected by private companies.
The authors also revisit the legal history of bulk telephone-record collection. They describe how the program began under a claim of presidential authority, was later tied to Section 215 of the Patriot Act and became publicly acknowledged after Edward Snowden's disclosures in 2013. A federal appeals court rejected the government's interpretation of Section 215 in 2015, and Congress subsequently passed the USA Freedom Act. The essay says that law ended the earlier indiscriminate collection model while still permitting extensive acquisition of telephone records.
Other collection programs remain in place. The authors cite the National Security Agency's Upstream program, which intercepts communications at telecommunications infrastructure and was brought under Section 702 of the Foreign Intelligence Surveillance Act amendments. They note that the NSA ended one form of content searching in 2017 after pressure from the surveillance court, but argue that broad collection continues and inevitably captures communications involving people in the United States.
Their central criticism is not that every surveillance technique has no investigative value. Rather, they say the government has not produced a comprehensive public accounting of costs, benefits and alternatives, or demonstrated that bulk methods prevented attacks that targeted work could not have stopped. They make a similar argument about domestic policing and immigration enforcement, where vendors and agencies often cite anecdotes or activity counts rather than independently tested public-safety outcomes.
The essay is an argument by two longtime surveillance critics, not a new government policy announcement. Its immediate news value lies in the authors' effort to mark 25 years since the attacks with a policy challenge: subject mass-surveillance programs to evidence-based review, weigh any benefits against effects on rights and freedoms, and abandon the assumption that collecting more information necessarily creates greater safety.